IntroToBurp
Try here to find the flag
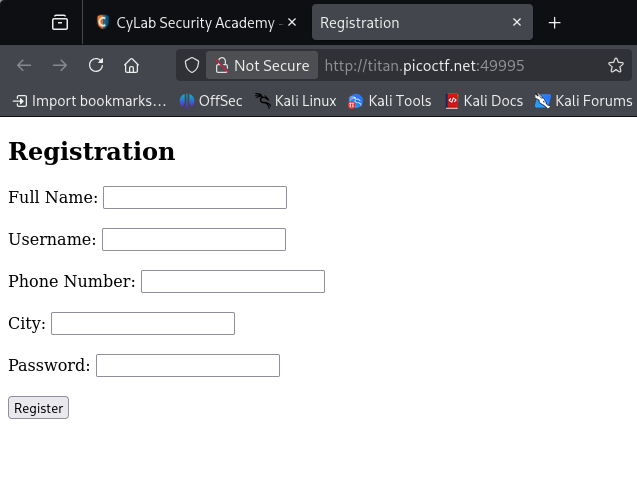
Use Burp Suite to intercept the request. The POST request includes an OTP in its body. Removing the OTP from the request body bypassed the check in this challenge.
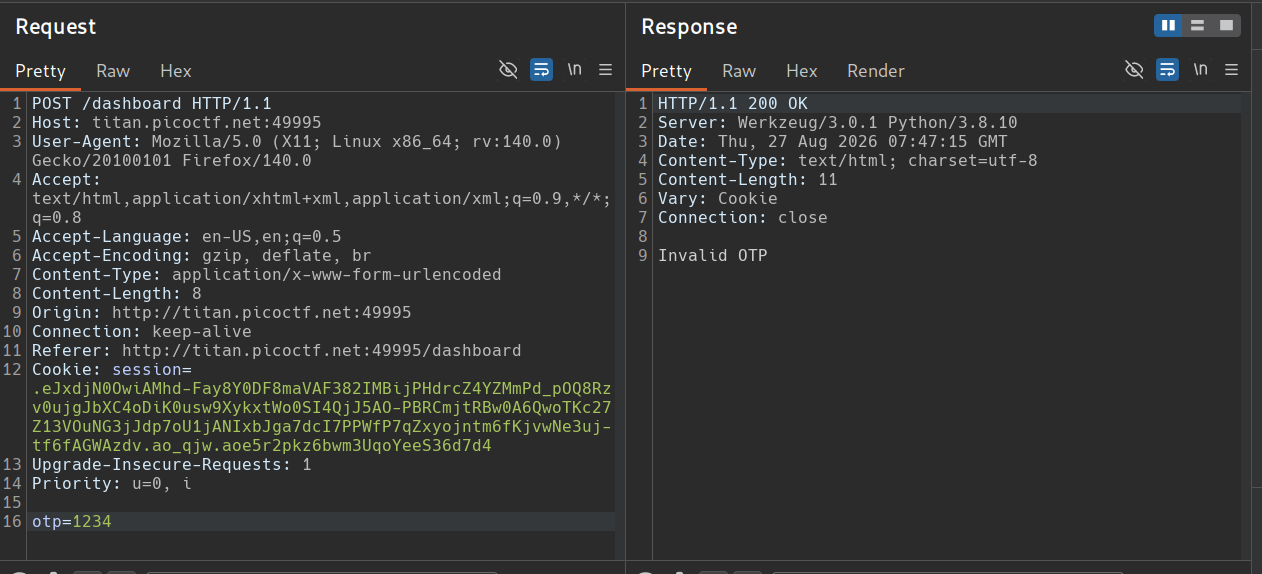
This gives you access to /dashboard.
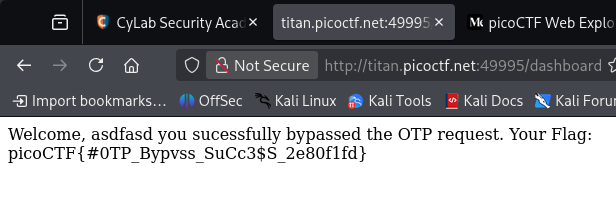
DONE!!
This post is licensed under CC BY 4.0 by the author.