PW Crack 3
Can you crack the password to get the flag? Download the password checker here and you'll need the encrypted flag and the hash in the same directory too. There are 7 potential passwords with 1 being correct. You can find these by examining the password checker script.
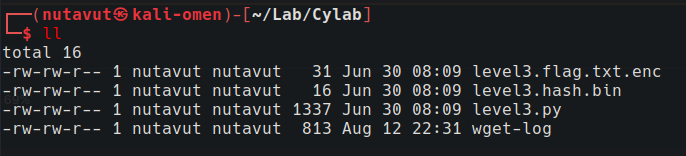
Download all the files.
chmod +x level3.py
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
58
59
60
61
62
63
64
65
66
67
68
69
70
71
72
73
74
75
76
77
78
79
80
import hashlib


### THIS FUNCTION WILL NOT HELP YOU FIND THE FLAG --LT ########################

def str_xor(secret, key):

#extend key to secret length

new_key = key

i = 0

while len(new_key) < len(secret):

new_key = new_key + key[i]

i = (i + 1) % len(key)

return "".join([chr(ord(secret_c) ^ ord(new_key_c)) for (secret_c,new_key_c) in zip(secret,new_key)])

###############################################################################


flag_enc = open('level3.flag.txt.enc', 'rb').read()

correct_pw_hash = open('level3.hash.bin', 'rb').read()


def hash_pw(pw_str):

pw_bytes = bytearray()

pw_bytes.extend(pw_str.encode())

m = hashlib.md5()

m.update(pw_bytes)

return m.digest()


def level_3_pw_check():

user_pw = input("Please enter correct password for flag: ")

user_pw_hash = hash_pw(user_pw)

if( user_pw_hash == correct_pw_hash ):

print("Welcome back... your flag, user:")

decryption = str_xor(flag_enc.decode(), user_pw)

print(decryption)

return

print("That password is incorrect")


level_3_pw_check()


# The strings below are 7 possibilities for the correct password.

# (Only 1 is correct)

pos_pw_list = ["f09e", "4dcf", "87ab", "dba8", "752e", "3961", "f159"]
The code lists seven possible passwords. The hash_pw function hashes each password with MD5.
1
2
3
4
5
6
7
8
9
10
11
if( user_pw_hash == correct_pw_hash ):

print("Welcome back... your flag, user:")

decryption = str_xor(flag_enc.decode(), user_pw)

print(decryption)

return

print("That password is incorrect")
These lines show that you can identify the correct password by comparing its hash with correct_pw_hash. Start by inspecting level3.hash.bin.
Use bvi level3.hash.bin.
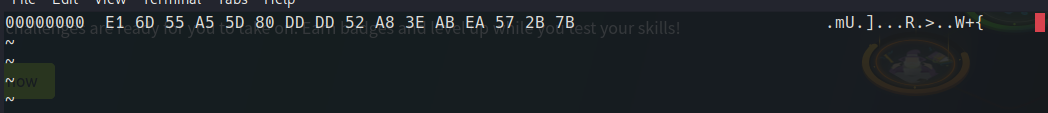
e16d55a55d80dddd52a83eabea572b7b
Find the password whose MD5 hash matches this value.
Use this one-line Bash command:
for x in f09e 4dcf 87ab dba8 752e 3961 f159; do printf '%s' "$x" | md5sum; done
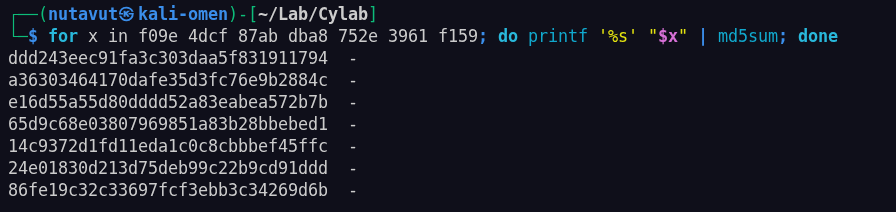
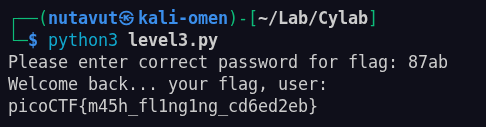
The MD5 hash of 87ab was e16d55a55d80dddd52a83eabea572b7b, so 87ab was the correct password.
Then run level3.py.