Disk,disk,sleuth!
Use srch_strings from the sleuthkit and some terminal-fu to find a flag in this disk image.
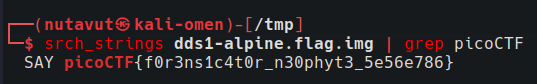
Download the file and decompress it with gunzip. Then use srch_strings with grep picoCTF to find the flag.
srch_strings extracts readable text from the disk image, and grep keeps lines containing the flag prefix. This can reveal plaintext stored in the image without mounting its filesystem.
This post is licensed under CC BY 4.0 by the author.